[munin]アラートメールを送る

muninでしきい値を超えた時にメールを送れるようなので設定してみました。

<環境>
Centos 6.3
Munin version 2.0

ハードディスク容量でテストしてみます

今の状態は


# munin-run df
_dev_vda3.value 2.72093653752988
_dev_shm.value 0.0282237832413447
_dev_vda1.value 21.9097563361532

設定を確認


# munin-run df config
graph_title Disk usage in percent
graph_args --upper-limit 100 -l 0
graph_vlabel %
graph_scale no
graph_category disk
_dev_vda3.label /
_dev_vda3.warning 92
_dev_vda3.critical 98
_dev_shm.label /dev/shm
_dev_shm.warning 92
_dev_shm.critical 98
_dev_vda1.label /boot
_dev_vda1.warning 92
_dev_vda1.critical 98

設定を変えます


# vim /etc/munin/munin.config

+ contact.email.command mail -s "Munin ${var:host}" sample@example.com
+ contact.email.max_messages 10
+ contact.email.always_send warning critical

[localhost]
    address 127.0.0.1
    use_node_name yes
+    df._dev_vda3.warning 1
+    df._dev_vda3.critical 2

テストメールを送ってみる


sudo -u munin sh -c "/usr/share/munin/munin-limits --contact email --force"

下記のようなメールが届きます


localhost :: localhost :: Disk usage in percent
	OKs: /boot is 21.91, /dev/shm is 0.03, / is 2.72.

localhost :: localhost :: Connections through firewall
	OKs: Total is 14.00.

localhost :: localhost :: Inode usage in percent
	OKs: /boot is 0.07, /dev/shm is 0.04, / is 1.62.

localhost :: localhost :: File table usage
	OKs: open files is 1184.00.

localhost :: localhost :: Disk latency per device :: Average latency for /dev/vda
	OKs: Read IO Wait time is 0.02, Write IO Wait time is 0.00.

localhost :: localhost :: eth0 errors
	OKs: errors is 0.00, errors is 0.00.

しきい値は、いい値に変更してください
[eccube]このウェブページにはリダイレクト ループが含まれていますのエラー

eccubeの環境を、ローカル構築中できた
と思って、管理画面にアクセスするとエラー発生

「このウェブページにはリダイレクト ループが含まれています」
.htaccessをみたけど、異常無し

調べてみると


vim data/config/config.php

define('ADMIN_FORCE_SSL', true);
↓
define('ADMIN_FORCE_SSL', false);

で直りました

「sudoers ファイル内にありません」のエラー

sudo 実行時にエラーが出た


testuser は sudoers ファイル内にありません。この事象は記録・報告されます。

突然、どうした。

id コマンドをうつと
uid=500(testuser) gid=500(testuser) 所属グループ=500(testuser),48(apache)

wheelグループがいない…

rootで入って
su root

グループを追加する
usermod -G apache,wheel testuser

複数グループのときは、カンマで区切って登録しないと
一つになってしまいます

testuserに戻って
exit;

sudoできたら直りました

シンボリックリンク攻撃を基礎からおさらい

シンボリックリンク攻撃を超基礎から整理します

<環境>
Centos
Apache 2.2.15

まずは、Apacheでのアクセス権限について整理


/var/www/html/test/index.html

というフォルダを参照するとき
apacheグループ所属のapacheユーザーがアクセスにきます

WEBブラウザで参照するときに必要になるのは


/var/www/html/test/ → x 実行権限
/var/www/html/test/index.html → r 読み取り権限

シンボリックリンク攻撃の一例を試してみます

下記の通り、ファイルがあるとして


drwx------   apache apache test
drwx------   apache apache test/index.php
drwx-----x   user   user   test2
drwx---r--   user   user   test2/index.php

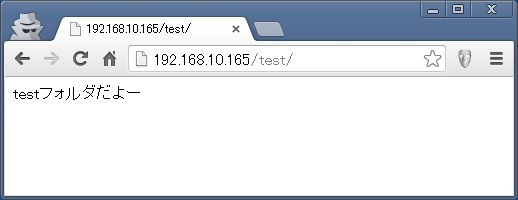
http://(server ip)/test/index.php
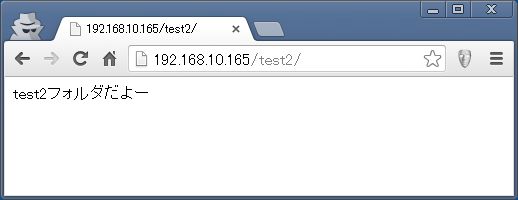
は見れるし

symlink1

http://(server ip)/test2/index.php
も見れます

symlink2

test/index.phpのソースは普通は見れませんが


cd test2
ln -s ../test/index.php test.txt

とシンボリックリンクを作って


drwx------   apache apache test
drwx------   apache apache test/index.php
drwx-----x   user   user   test2
drwx---r--   user   user   test2/index.php
lrwxrwxrwx   user   user   test.txt -> ../test/index.php

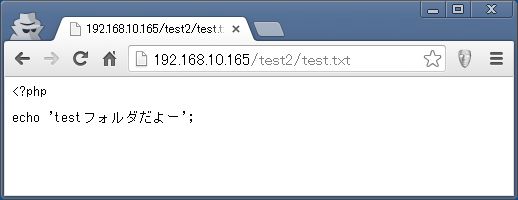
http://(server ip)/test2/index.txt
とすると

symlink3

ソースが見えてしまいます。
恐ろしい…

防ぐにはhttpd.confか.htaccessでのFollowSymLinksを無効にすればいいです


Option -FollowSymLinks

また、SymLinksIfOwnerMatchを有効にすると
所有ユーザーが同じファイルのシンボリックリンクが有効になります


Option -FollowSymLinks SymLinksIfOwnerMatch

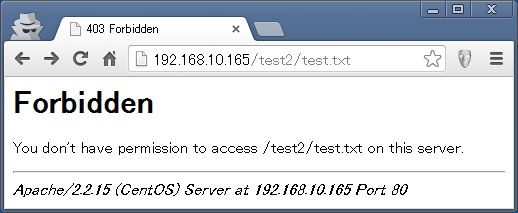
上記例での http://(server ip)/test2/index.txt
のアクセスは


drwx------   apache apache test/index.php
lrwxrwxrwx   user   user   test.txt -> ../test/index.php

所有ユーザーが違うので

symlink4

アクセスできなくなります